🧭 The decision that comes before the chatbot
OpenAI’s September 8, 2026 announcement of up to $5 million in independent research grants on generative AI and teen development is a useful interruption for website teams. The announcement does not settle what AI does to young people. It says the effects may depend on what teens use AI for, how they engage with it, their circumstances, and the support around them. That uncertainty is the point. A small business does not need to wait for every research question to be answered before making one basic product decision: who, by age, is this feature actually for?
Many teams begin in the opposite order. A chat widget promises faster answers. A recommendation module promises more relevant products, articles, or courses. Someone activates a vendor feature, adds a short privacy-policy sentence, and assumes the rest is a content problem. But chat and recommendation systems change the relationship between a visitor and a site. They invite prompts, infer interests from behavior, and can influence the next thing a person sees or does. When the visitor may be a child or teenager, an undefined audience is a design gap with privacy, safety, and operational consequences.
An age boundary is not a decorative age gate. It is a documented decision about the youngest people a feature is designed to serve, the information it may receive, the protections that apply, and the route offered to everyone else. It should exist before a team writes prompts, connects analytics, imports a product catalogue, or measures conversion.
For a local retailer, clinic, school supplier, hospitality business, publisher, or service firm, this can sound larger than the feature. It is usually smaller and more concrete. Define the audience. Map the data. Set default access. Test the handoff. Keep a record of the choice. The work is less exciting than a conversational demo, but it is where a responsible launch begins.
📌 Age is a product requirement, not a footer link
A website’s age boundary answers several questions that teams often blur together. Is the main site intended for adults, teenagers, children, or a mixed audience? Is the AI feature available to every visitor, only logged-in customers, or only a specified age group? Does the business know a visitor’s age, or is it simply choosing not to make the feature child-directed? What happens when a user indicates that they are below the threshold? These are product requirements because each answer changes the interface, data flow, vendor configuration, support script, and measurement plan.
The U.S. Federal Trade Commission’s COPPA guidance is a practical starting point for teams serving the United States. COPPA concerns commercial websites and online services directed to children under 13 that collect, use, or disclose personal information, as well as general-audience services with actual knowledge that they are doing so. The FTC lists information such as online contact details, persistent identifiers, photos, videos, audio containing a child’s image or voice, and sufficiently precise geolocation among the categories that can be personal information. A chat box can receive names, phone numbers, school details, images, voice transcripts, or free-form personal disclosures. A recommendation feature can rely on identifiers and behavior over time. Calling either tool “just a widget” does not change those flows.
COPPA is not a universal age-design manual, and a global site may face other legal regimes. Still, its framing helps expose a common mistake: treating age as a demographic field to collect because marketing would like it. An age boundary should reduce unnecessary collection. If a business does not need to operate an AI feature for children, the safer operational choice may be to keep that feature unavailable to them rather than gather more personal data in an attempt to personalize it.
UNICEF’s guidance on AI and children reaches beyond a single privacy rule. Its child-centred requirements include safety, data and privacy protection, non-discrimination and fairness, transparency and accountability, children’s best interests, inclusion, and an environment that prepares children for AI. Those are not a plug-in checklist. They are questions a website owner can use to examine a proposed feature before it appears in production.
A clear boundary also stops teams from using vague labels. “Family-friendly” does not tell an engineer whether a 10-year-old can use the recommender. “For students” does not say whether the service is designed for 12-year-olds, 16-year-olds, adult learners, or all of them. “General audience” does not excuse a team from deciding what it will do when it knows a young child is using the feature. A precise policy is easier to implement and easier to explain.
The business question is not whether a chatbot looks harmless. It is whether the company can explain, in plain language, who may use it, what it receives, what it does with a young person’s information, and where a young person goes when the feature is unavailable. If those answers are missing, the launch is not ready.
🧒 Teen research is a prompt to separate children from teenagers
OpenAI’s grant programme explicitly concerns young people aged 13 to 17. Its research topics include emotional development and well-being, social development and relationships, patterns of use across ages and contexts, and mitigations such as safeguards, age-appropriate design, AI literacy, and parental or educator support. The programme asks for independent work, and it describes proposed research rather than final findings. That distinction matters. A website should not cite the announcement as proof that a particular chat feature harms or benefits teens. It is evidence that important questions remain open and that age and context deserve specific attention.
It also makes one useful editorial point: “young users” is too broad to guide a product. A pre-teen, a 13-year-old, and a 17-year-old may all be minors, but a team should not assume they have identical needs, permissions, or reasons for using a service. The legal threshold in the FTC material is under 13. The OpenAI grant announcement focuses on ages 13 to 17. Those scopes are different. A single checkbox labelled “I am over 13” cannot do the reasoning for a business.
For a small website, the immediate decision can be modest. An online shop selling adult skincare might decide that its AI product finder is for adults only and show a standard catalogue to everyone else. A tutoring business that welcomes teenagers might decide that its answer assistant is limited to course-navigation questions, avoids collecting sensitive details, and hands complex questions to a human contact. A youth-oriented publisher might decide that recommendations use only the current page context rather than an account-level behavioral profile. Each choice should be written as a sentence that a developer, customer-support worker, and visitor can understand.
Age boundaries should not turn into a performance of certainty. A self-reported date of birth or age band has limitations. It may be appropriate in some settings and inappropriate in others. The key operational point is consistency: the amount of age assurance a team seeks should be proportionate to what the service does and what information it collects. A site should not demand an identity document merely to suppress a chat widget. Nor should it invite a child into a data-intensive conversational experience while pretending that an ambiguous disclaimer solves the problem.
When a user falls outside the permitted age range, the alternative matters. A blank refusal can send someone to search engines, social media, or an unmoderated form. Offer a simple route instead: browse pages, read an FAQ, contact customer support, ask a parent or teacher where appropriate, or use a clearly bounded non-personalized tool. This is service design, not a loophole.
The grant announcement also calls attention to the role of families, schools, communities, and technology providers. A small business cannot control every part of a teenager’s environment. It can control whether its own website assumes that a conversational system should substitute for a person, whether the system is allowed to solicit personal stories, and whether staff know how to respond when a conversation signals distress or risk.
🧱 Build the boundary into the service, not only the terms
A boundary that lives only in a terms-of-use page will fail under ordinary use. The visitor meets the actual rule at the point where the feature is offered. That means the rule needs visible interface behavior, backend controls, vendor settings, and a support process that match each other.
Start with an inventory. List every AI-assisted surface on the website, including the obvious chat assistant and recommender, but also automated search, quiz results, customer-service routing, generated product descriptions, image analysis, and third-party embedded tools. For each surface, write down what a visitor can input, what the system observes automatically, what leaves the site, what is stored, and who can see it. Do not accept a supplier’s broad statement that it is “privacy focused” as a substitute for this map. The FTC guidance says operators of child-directed services must inquire into the information collection practices of third parties that can collect through their service. Even when a feature is not child-directed, the discipline is useful.
Next, choose an access pattern. There are several workable patterns, depending on the site and its audience:
- Adults-only AI feature: The page remains accessible, but chat and personalized recommendations are not offered below the stated threshold. The fallback is ordinary navigation, search, or staff contact.
- Teen-accessible bounded feature: A teenager can use narrowly defined functions, such as finding a public course page or choosing a product category. Free-form personal advice, saved conversation history, and sensitive profiling are excluded.
- Child-directed service with a distinct compliance design: The business treats the service as directed to children and plans for the applicable consent, notice, data, security, retention, and third-party obligations. This is not an option to select casually.
- No AI interaction for uncertain audiences: A site serves a broad public and cannot confidently configure the feature for young visitors. It keeps human-written pages and conventional search instead.
The right pattern depends on the facts, not on which one sounds most modern. A business must also tell its team what it is not doing. If the chat feature is not a health, legal, educational assessment, or crisis service, that should be clear in its scope and response rules. If it cannot accept images, voice messages, contact details, or account information from young users, make the input design enforce that choice where possible.
A human route should be designed with equal care. “Contact us” is not enough if the form asks for a detailed story and sends it to the same unreviewed workflow. Give staff a short escalation guide: what the feature can answer, what it must not answer, what data should not be requested, and when the conversation must move to an adult support channel or a qualified service. The purpose is not to make employees diagnose a visitor. It is to stop an automated interface from becoming the only apparent listener.
🗣️ Conversation design changes what a visitor may disclose
Chat is different from a menu because it invites language. A visitor can ask a simple product question, then volunteer a full name, a photo, a location, a family problem, or a concern that has nothing to do with the business. Young users may not distinguish a company’s support bot from a person, a search box, a tutor, or a companion. UNICEF’s updated guidance specifically identifies AI companions used by children among the developments it addresses. That is enough reason for a business to examine the tone and scope of its own conversational interface.
Do not make the bot sound like a confidant when it is a sales or support tool. Avoid prompts that invite personal disclosure merely to increase engagement. A furniture retailer can say, “Tell me the room size and style you prefer,” rather than “Tell me about your home and what is stressing you.” A school-supplies site can ask for a grade level or subject only if it needs that information for a stated result, and it can offer browsing without an account. The same restraint applies to follow-up questions generated by the system.
Teams should set boundaries in the conversation specification before they set a personality. Define permitted topics, disallowed topics, prohibited data requests, and response routes. If the assistant cannot provide a reliable answer, it should say so and point to a relevant page or a human channel. It should not improvise authority, simulate a professional relationship, or encourage a visitor to keep a sensitive exchange secret.
Recommendation systems need similar attention, even though they do not speak. “People like you” can be a strong social cue. A system that ranks content based on observed behavior can make assumptions a visitor cannot see or correct. UNICEF’s guidance includes transparency, explainability, accountability, fairness, and non-discrimination. For a small website, the practical translation is simple: be able to explain at a sensible level why a person is seeing a recommendation, provide a non-personalized alternative, and make it possible to change or stop the recommendation setting.
The FTC’s definition of personal information includes persistent identifiers that recognize a user over time and across websites or online services. Teams should therefore ask their analytics and recommendation vendors direct questions. Does the tool use cookies or another identifier? Is data combined across customers or services? Is the feature trained on prompts? Can logs be disabled, shortened, or isolated? Which sub-processors receive the data? A vendor’s answer belongs in the launch record, along with the date it was checked.
“Personalized” should never become a reason to collect a young visitor’s story. For many small sites, context-based recommendations are enough. Suggest a matching accessory because it fits the item currently viewed. Show related articles because they share a topic tag. Let the person select interests in the moment without creating a durable behavioral record. These choices can be less intrusive and easier to explain.
🔍 Put the boundary where users and systems can act on it
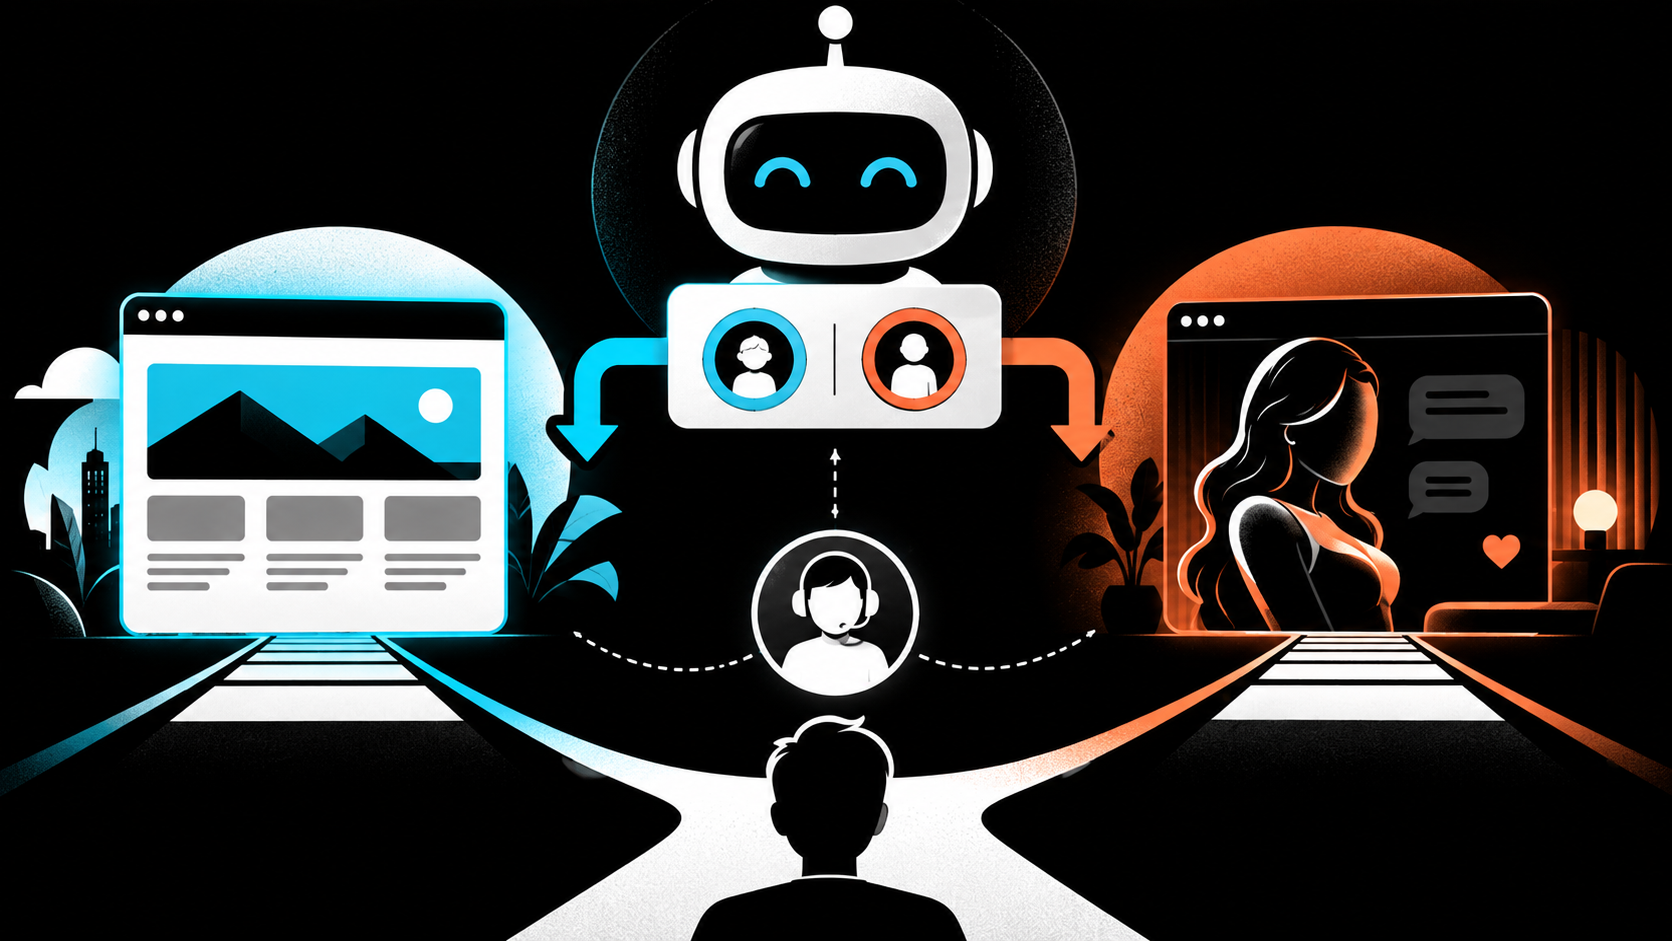
The best age boundary is visible, brief, and connected to a real consequence. It does not need legal theatre. At the entry to chat or personalized recommendations, state who the feature is for and what happens if the user is outside that group. If the site asks for age information, explain why it is asking and do not reuse the answer for unrelated marketing by default.
A simple interface might present two paths: “Continue to general site” and “Use adult customer assistant.” A teen-accessible feature might instead say that it helps find public information and does not replace a teacher, parent, professional, or emergency service. The exact wording must match the actual service. Promising protections that a vendor configuration does not deliver is worse than saying less.
The backend must enforce the same decision. If a user states or is known to be below the feature’s threshold, do not merely hide a button while leaving the endpoint accessible through an account page, embedded script, or mobile view. Apply the rule to account eligibility, session creation, API calls, saved history, and recommendation-profile creation. Check logged-out and logged-in journeys separately. Check the experience when a user changes a birthday, clears cookies, opens a private browser window, or reaches the feature through a shared link.
Keep age data separate from the urge to profile. In some cases, a business may only need a coarse result such as “eligible” or “not eligible,” rather than a full date of birth kept indefinitely. Data minimization is a practical habit: collect the least information that can operate the chosen design, retain it only for the stated purpose, and review whether it is still needed. The FTC guidance requires covered operators to retain children’s personal information only as long as reasonably necessary for the collection purpose and to delete it using reasonable measures. Even beyond COPPA’s scope, retention limits make an AI feature easier to govern.
The privacy notice, help centre, vendor contract, and user interface must not contradict each other. Someone on the support team should be able to answer: Is chat history saved? Can it be deleted? Is it used to improve a system? Are recommendations based on a current visit, an account, or both? What happens if a parent asks for access or deletion? The team may need legal advice for the jurisdiction and product in question, but it does not need legal advice to recognize that these questions require owners.
Accessibility belongs here too. An age prompt that cannot be read by a screen reader, a refusal that disappears too quickly, or a fallback that works only with a mouse is not a completed boundary. UNICEF includes inclusion among its requirements for child-centred AI. Test the path with the same care given to checkout or booking forms.
🧪 Test the system for ordinary mistakes, not just model answers
A pre-launch test should cover more than whether the chatbot produces polite text. The risk is often in the system around the answer: a form field, stored transcript, embedded tracker, recommendation profile, support handoff, or staff workflow.
Create a small test set that reflects the boundary the team has chosen. Use fictional, non-sensitive prompts. Try a visitor who identifies as under the threshold, one who is 13 to 17 where that audience is supported, and an adult. Test a visitor who attempts to enter a phone number, address, school name, image, audio file, or a personal crisis statement. Test whether the assistant solicits more detail, whether the application saves the exchange, and whether the right alternative route appears. Record the result and the person responsible for fixing failures.
For recommendations, test the site with a new browser, a returning account, and an account that has opted out of personalization. Inspect whether the system still makes personalized claims after opt-out, whether a child-restricted account receives the same data-heavy modules, and whether the explanation link describes the actual behavior. If the team cannot inspect the vendor’s output or control its collection, that is a reason to reconsider the integration.
OpenAI’s Astra announcement is about frontier cybersecurity capabilities rather than child development, but it offers a relevant operating lesson. The company describes delaying parts of development and release while it strengthened and tested protections, and it describes layered safeguards, monitoring, and limits on advanced access. A small business is not running a frontier-model safety programme. It can still adopt the underlying discipline: capability should not outrun controls, and a feature can be held back while the team tests the conditions needed for release.
Testing needs a stop rule. Decide in advance what would block launch. Examples include inability to prevent a restricted user from opening the chat session, a vendor that cannot describe data retention, a bot that requests unnecessary personal details, no workable parent or support response, or analytics that continue after the supposed restriction. The correct response to a failed control is to disable or narrow the feature, not to rewrite a reassuring sentence.
Review after launch, too. Logs can show patterns such as repeated attempts to access a restricted feature, unhandled questions, or staff escalation gaps. Review aggregate operational signals without turning that review into surveillance of young users. When a product, model, plugin, privacy setting, or vendor contract changes, run the boundary tests again. The feature that launched safely is not automatically safe after a new integration.
⚖️ Assign owners before a problem arrives
An age boundary crosses roles. If everyone owns it, nobody does. A lean team can assign clear responsibility without creating a new committee. The website owner decides the intended audience and business purpose. The developer implements access and data controls. The privacy or legal adviser reviews applicable obligations. The customer-support lead owns the handoff language. The marketing lead ensures campaigns do not direct children toward a feature the product has restricted. The vendor manager keeps records of third-party terms and settings.
Put this into a one-page launch note. It can contain the feature name, purpose, intended age group, unsupported users, allowed inputs, prohibited inputs, data collected, data sent to vendors, retention setting, recommendation logic, disclosure text, fallback route, escalation owner, test date, and review date. This is not bureaucracy for its own sake. It gives the team a shared version of the service they are actually operating.
The note should distinguish a legal requirement from a voluntary product choice. For example, the FTC’s COPPA materials explain obligations for covered operators, including clear privacy policies, direct notice and verifiable parental consent in relevant circumstances, parental access and deletion rights, security measures, retention limits, and limits on conditioning participation on unnecessary information. A business should seek qualified advice where its service, audience, or geography may trigger specific duties. It should not claim that a broad internal policy makes it compliant everywhere.
UNESCO’s Guidance for Generative AI in Education and Research offers a wider public-interest frame for teams working around young people. It calls for an age limit for independent conversations with generative AI platforms and for strong data protection and privacy safeguards. For a small website, such principles become useful only when they change a concrete decision. Proportionality can mean choosing a related-content list over a behavioral profile. Human oversight can mean giving staff authority to pause a bot. Accountability can mean recording who approved a vendor setting and who checks it next quarter.
Vendor due diligence deserves plain questions, not vague assurances. Ask what data the tool receives from the browser and server, whether prompts or events are retained, whether content is used for training, how deletion requests work, what security controls apply, which other companies process data, and what age-related configurations exist. Ask whether the system can be limited by account type or context. Save answers and contracts in a place that survives staff turnover. If the vendor cannot answer a question central to the boundary, the business has learned something material before exposing visitors to the feature.
✅ A practical launch standard for small website teams
The decision to use AI chat or recommendations should begin with a sentence, not a script: “This feature is for [defined audience], it does [defined task], it receives [defined data], and people outside that boundary can [defined alternative].” If that sentence is hard to write, the feature is too vague to launch.
Use the following standard before enabling it:
- Name the audience and the age boundary for the specific feature, not merely the whole website.
- Map every input, identifier, transcript, event, vendor, and retention setting involved in the user journey.
- Choose the least data-intensive design that can deliver the stated task.
- Make the boundary visible at the point of use and enforce it in the backend, accounts, sessions, and embedded versions.
- Give restricted or uncertain users a useful non-AI route instead of a dead end.
- Set conversational rules that avoid unnecessary personal disclosure and specify human escalation.
- Provide a non-personalized recommendation path and an understandable explanation of recommendation behavior.
- Test child, teen, adult, logged-out, logged-in, opt-out, and error paths with fictional data.
- Document ownership, vendor answers, approval, and a scheduled review date.
- Pause the feature when the team cannot verify a control that the chosen boundary depends on.
OpenAI’s September research grants are a reminder that product teams should resist simple stories about teenagers and generative AI. The relevant questions include age, developmental stage, purpose, culture, support, safeguards, and design. A small business cannot resolve that research agenda. It can avoid adding confusion on its own site.
A clear age boundary gives a team a way to make choices before the chatbot becomes the default front door or the recommender becomes invisible infrastructure. It turns a broad aspiration to “use AI responsibly” into decisions a visitor can encounter and a staff member can defend. That is a sturdier starting point than launching first and trying to discover the audience afterward.
Sources: https://openai.com/index/teen-development-research-grants/ | https://openai.com/index/path-to-astra/ | https://www.unicef.org/innocenti/reports/policy-guidance-ai-children | https://unesdoc.unesco.org/ark:/48223/pf0000386693 | https://www.ftc.gov/business-guidance/resources/complying-coppa-frequently-asked-questions


