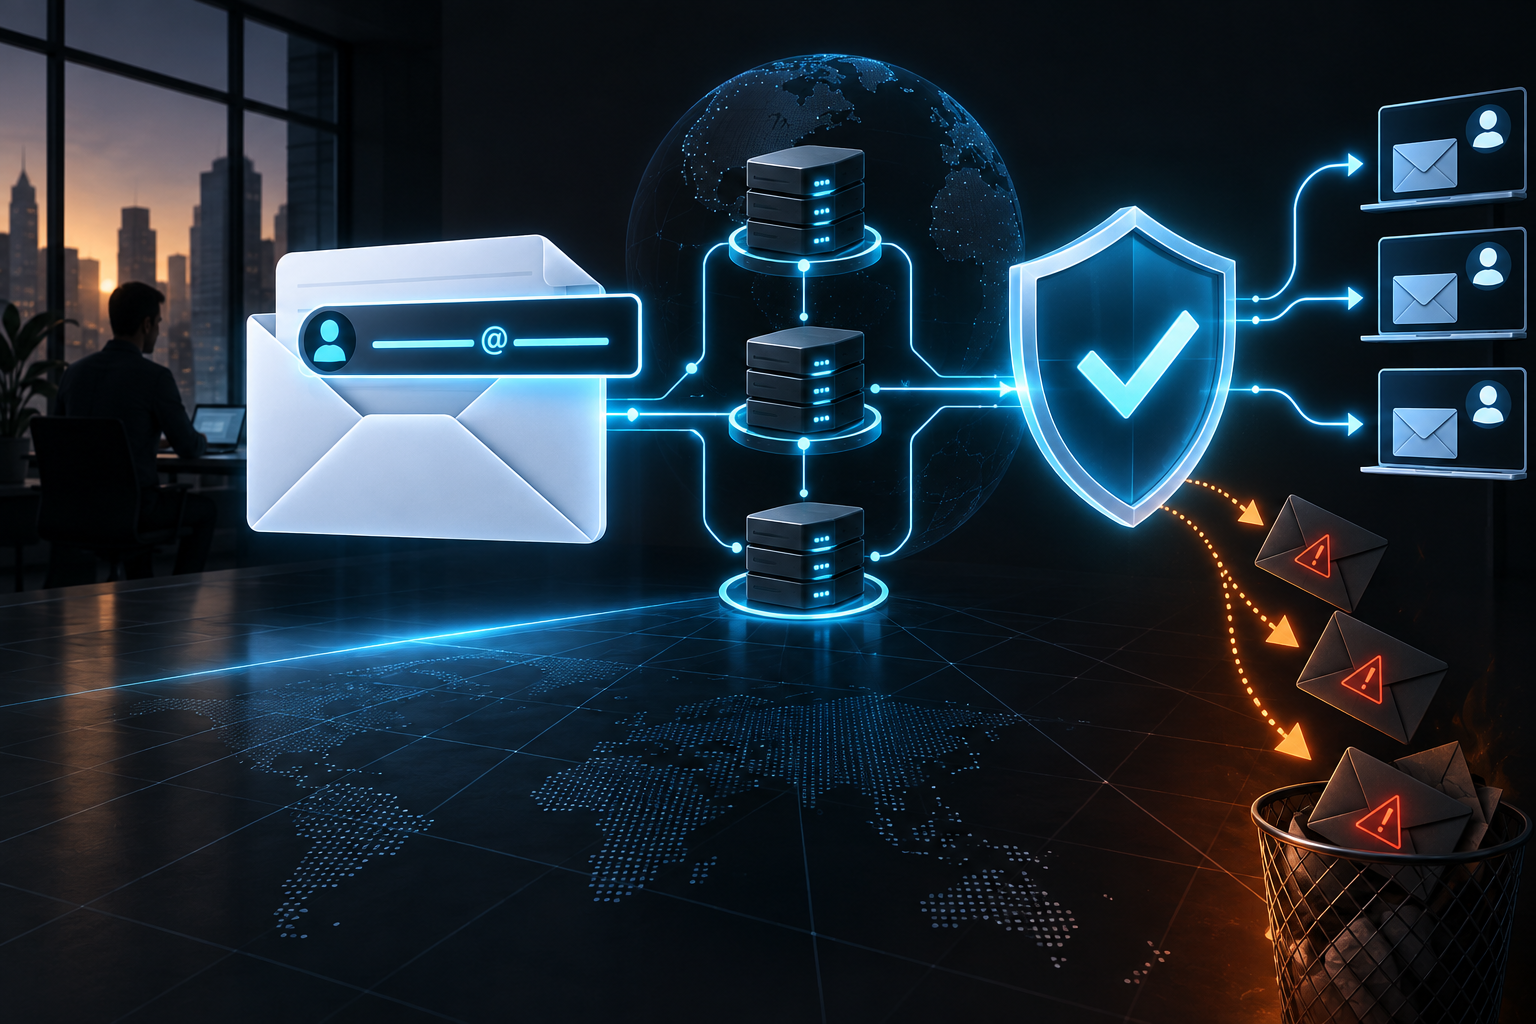
✉️ The email problem customers never see
A customer sees a familiar name in the From line and a domain they recognise. The message may be a receipt, appointment reminder, quote, password reset, or support reply. They do not see the checks performed before it arrives. They cannot tell whether a booking platform is authorised to send for the business, whether the visible From address aligns with the authentication behind it, or whether somebody else is trying to use the same domain.
That hidden layer makes email authentication easy to defer. The website is live, staff mail works, invoices leave the accounting platform, and campaigns appear to send. Nothing seems broken until legitimate mail lands in spam, a provider changes its setup, or an impersonating message reaches a customer under the business’s name.
DMARC, or Domain-based Message Authentication, Reporting, and Conformance, gives a domain owner a way to publish instructions for mail claiming to be from its domain. It builds on SPF and DKIM, then adds an alignment test: an authenticated identity must correspond with the domain displayed in the From field. The policy tells participating receivers how the owner wants failures handled and where reports should go. The model is described by the DMARC overview and RFC 7489.
For a small business, this is less about making every message perfect in a day than establishing control. Someone must own the domain, know the legitimate senders, and take the domain from observation to an enforceable policy. No DMARC record means no published path. A record that remains indefinitely at observation publishes a signal, but not a completed control.
The operational pressure is already real. Google requires baseline authentication and sender practices for mail sent to personal Gmail accounts. It imposes additional requirements on bulk senders, which it defines as sending close to 5,000 or more messages to Gmail accounts in a day. Yahoo likewise separates all senders from bulk senders and includes DMARC in its authentication expectations. A business need not think of itself as an email marketer to be affected. A seasonal campaign, a product launch, or a high-volume notification run can change the category of traffic in a day.
Email is also distributed. One domain may be used by Microsoft 365 or Google Workspace, website forms, accounting software, a customer relationship platform, an ecommerce provider, a help desk, and a newsletter tool. Each might be authorised. Each might authenticate differently. Customers see one brand domain and will not disentangle that infrastructure for the business.
The first decision is simple: treat the sending domain as an asset with an owned authentication policy, not as a label that any connected service may use indefinitely.

🔎 A fast snapshot of the sender rules
Google and Yahoo do not treat DMARC as an abstract security exercise. Their guidance connects authentication to delivery and responsible sending. That matters because a business often receives partial advice, such as “add SPF,” without being told which control applies to which mail stream.
Google’s Email sender guidelines say that senders to personal Gmail accounts need SPF or DKIM authentication, valid forward and reverse DNS records, TLS for transmission, and a low spam rate. Bulk senders must use SPF, DKIM, and DMARC. Google specifies a minimum DMARC policy of p=none for that category, and requires the visible From domain to align with either SPF or DKIM.
Yahoo’s sender best practices similarly say all senders should authenticate with SPF or DKIM, while bulk senders should use SPF, DKIM, and DMARC. Yahoo defines bulk senders as those sending more than 5,000 messages per day to Yahoo Mail accounts. Its guidance also covers unsubscribe handling for bulk and marketing mail, complaint rates, and valid DNS.
These pages are not a checklist to copy without context. They show why a domain is more than a mailbox name and why authentication is different from policy.
Sender control comparison
- SPF: Checks whether sending infrastructure is authorised for the relevant envelope-sender domain. It can identify approved infrastructure, but does not by itself prove the visible From identity.
- DKIM: Checks whether a message has a valid cryptographic signature associated with a domain. It can remain useful through some forwarding paths if the message stays intact.
- DMARC: Checks whether SPF or DKIM passes and aligns with visible From, plus requested handling and reporting. It connects authentication to the brand domain the recipient sees.
SPF can pass for a domain different from the domain shown to the customer. DKIM can pass for a different domain too. DMARC asks whether at least one passing authenticated domain aligns with the RFC 5322.From domain. Authentication alone is not sufficient.
So the useful question is not, “Does our newsletter provider have SPF?” Ask: “When this provider sends with our domain in From, will either SPF or DKIM pass and align with that domain?” Apply the same test to invoices, support replies, form notifications, account messages, and internal systems that contact customers.
DMARC also does not solve unwanted mail, weak consent practice, or poor list management. Google and Yahoo place authentication beside low complaint rates, unsubscribe expectations, and sound DNS. DMARC gives the domain a clearer identity boundary; it does not make weak sending practices acceptable.
The short version:
- SPF and DKIM authenticate aspects of a message.
- DMARC requires an aligned pass from at least one of them.
- Google and Yahoo require DMARC for their bulk-sender categories.
p=noneis an observation stage, not the final level of protection.- Delivery, complaint handling, and subscription practice remain separate work.
🧾 What DMARC actually checks
DMARC is often called email authentication, but that is incomplete. It does not create a third signature. It evaluates SPF and DKIM results, tests alignment with the RFC 5322.From domain, applies the owner’s published policy, and can request reporting. RFC 7489 defines the process and record format.
The visible From address matters because it is the identity customers use to decide who sent a message. If it says [email protected], DMARC evaluates alignment against example.com.
SPF alignment compares the domain used by SPF, commonly associated with the SMTP MAIL FROM identity, with the visible From domain. DKIM alignment compares the d= domain in a valid signature with that same visible domain. DMARC passes when at least one mechanism both authenticates successfully and aligns.
“At least one” is important. A message need not have both SPF and DKIM pass DMARC. Maintaining both is still sensible: they assess different parts of mail flow and can fail for different reasons. Google and Yahoo call for both in their bulk-sender requirements.
RFC 7489 provides relaxed and strict alignment modes. Relaxed alignment permits organisational-domain matching; strict alignment needs an exact domain match. The adkim and aspf tags select the relevant mode. Those choices should follow a known mail design, not an assumption.
For example, a marketing platform might sign with d=mail.example.com while the visible From address is [email protected]. Under relaxed DKIM alignment, those domains can align because they share an organisational domain. Under strict alignment, they do not. Neither mode is universally correct. The business needs to understand its subdomains and choose deliberately.
DMARC publishes a requested disposition with the p tag:
- **
p=none:** No specific DMARC enforcement action. Use it to observe and collect reports. - **
p=quarantine:** Ask receivers to treat failing mail as suspicious and move it away from normal inbox handling. - **
p=reject:** Ask receivers not to accept failing mail.
The receiver still makes the delivery decision. RFC 7489 describes a DMARC policy as a request and permits local receiver policy. Do not promise that DMARC makes impersonation impossible or guarantees inbox placement. It makes the owner’s preferred treatment of unauthenticated, misaligned mail explicit to receivers that perform DMARC evaluation.
Use a chain of questions rather than a single-switch model:
- Does SPF pass?
- Does DKIM pass?
- Does at least one passing mechanism align with the visible From domain?
- If not, what policy did the domain owner publish?
- What does the receiving system decide under its own rules?
That chain explains why a successful test can mislead. One provider may sign correctly while an unrecorded legitimate sender does not. SPF may pass but fail alignment. Forwarding may change how SPF is evaluated. A report-led rollout reveals those differences before the business asks receivers to quarantine or reject failures.
DMARC records are DNS TXT records at _dmarc.example.com and usually start with v=DMARC1. RFC 7489 defines policy, aggregate-report, and failure-report tags, record discovery, external-report authorisation, and handling for malformed or multiple records. This is not mere housekeeping. DNS is where the business states its email identity policy. If nobody can safely change that record, nobody clearly owns the identity customers see.
🧭 Why publish-only is not a strategy
Publishing p=none is a sensible first move. It is not a finished strategy.
An observation policy lets the owner receive visibility into mail claiming the domain without asking receivers to quarantine or reject failures. That matters because the first reports often reveal legitimate senders that were not in anyone’s inventory: a form service, old application, finance platform, support tool, or provider configured by a former employee or agency.
CISA’s Binding Operational Directive 18-01 requires federal agencies within its scope to implement email security measures including DMARC and describes a progression toward p=reject. Its federal mandate does not directly govern a small business, but the implementation logic is useful: configure SPF and DKIM, monitor what the domain is doing, then enforce once legitimate traffic is understood.
Publish-only can become permanent for understandable reasons. Reports look technical. DNS and mail platforms have different owners. An agency runs campaigns. Someone fears that a stricter policy will interrupt invoices or support messages. Those are reasons to investigate carefully, not reasons to end the investigation.
At p=none, the owner asks receivers to take no particular enforcement action based on DMARC failure. Reports may expose failures, but the policy does not ask participating receivers to quarantine or reject them for the owner. Telemetry is useful; telemetry alone is not a control.
That does not mean jumping directly to p=reject. Applying a strict policy before approved senders are correctly configured can disrupt real mail. The appropriate path is staged, evidence-led, and owned by people able to repair mail flow.
- **Discover with
p=none:** Identify legitimate sending sources and assign report ownership. - **Correct while on
p=none:** Configure aligned SPF or DKIM for every approved sender, then test expected flows. - **Contain with
p=quarantine:** Resolve or isolate remaining legitimate failures and watch reports and important mail. - **Enforce with
p=reject:** Keep monitoring and control changes to approved senders.
This is governance as much as DNS. Document each permitted sender, business owner, technical owner, sending purpose, applicable subdomain, and authentication method. That record stops a common failure: a new tool sends with the business domain before anyone verifies alignment.
Subdomains need an explicit decision. RFC 7489 includes the sp tag for a subdomain policy where an explicit subdomain record does not exist. A business can separate streams, such as news.example.com for newsletters or receipts.example.com for transactional mail. That can make attribution cleaner, but it does not remove the need to understand every sender.
The case against indefinite p=none is clarity, not panic. Once legitimate senders are known and authenticated, the domain owner can ask receivers to treat failures differently. If senders are not known, the reports identify the work left. Both outcomes are better than assuming a DNS record solved the problem.
🛠️ The records your domain needs
The records are short; the preparation behind them is not. Start with a sender inventory, turn it into DNS and platform settings, then check it repeatedly.
- SPF TXT record in domain DNS: Lists authorised mechanisms for the relevant SPF identity. Ask which services may send with the domain or envelope-sender domain.
- DKIM TXT record at a selector-specific name: Publishes a provider signature’s public key. Confirm each sender has enabled DKIM and record its
d=domain. - **DMARC TXT record at
_dmarc.example.com:** Publishes policy, alignment, and report addresses. Assign someone to review reports. - Return-path setting in the platform: Influences SPF identity and possible alignment. Check whether the envelope sender aligns with visible From.
- From-address setting in the platform: Defines what customers see. Use a domain the business owns and authenticates.
SPF is a DNS TXT record. For DMARC, the vital point is that an SPF pass contributes only when it aligns with visible From. A provider may ask for an include mechanism or a custom return-path domain. Follow its documented steps, then test with the actual From address customers receive.
SPF has limits. Its evaluation has DNS lookup limits, so a record stuffed with inherited provider includes can fail. Review it instead of adding entries indefinitely. Remove services that are no longer authorised. Do not publish multiple SPF TXT records for one domain: that can result in an SPF permerror, not a combined permission list.
DKIM is normally enabled in the sending platform. The provider supplies a selector record, which the business publishes, and signs outgoing mail. Confirm success through received headers or provider verification. Note the signing domain. A valid signature from an unrelated provider domain may authenticate for that provider, but may not align with the business’s visible From domain.
DMARC joins this work. A starter shape might be:
v=DMARC1; p=none; rua=mailto:[email protected]It is an illustration, not a copy-and-forget configuration. The report address must be monitored. RFC 7489 specifies aggregate report URIs and the authorisation required when reports go to a different domain.
A record may include pct, adkim, aspf, sp, ruf, and fo. Use them because there is an operational reason, not because an example lists them:
psets the requested policy.ruanames aggregate-report destinations.rufnames failure-report destinations, subject to receiver support and RFC 7489 privacy considerations.adkimandaspfselect strict or relaxed alignment.spcan set a subdomain policy.pctcan stage enforcement for a percentage of failing mail.
The most valuable record may sit beside DNS: a live sender inventory.
Build a sender inventory with these fields for each approved source:
- Sending source and business purpose.
- Visible From domain.
- SPF and DKIM alignment result, verified from headers and provider settings.
- A named operational owner and a review date.
Apply it to the mail host, billing provider, customer platform, website application, and every other service that sends as the domain.
Replace every “confirm” entry with a real answer before strict enforcement. Record review dates. The same table makes vendor changes safer when a provider changes a DKIM selector, sending region, or DNS instruction.
📊 Read reports before you tighten policy
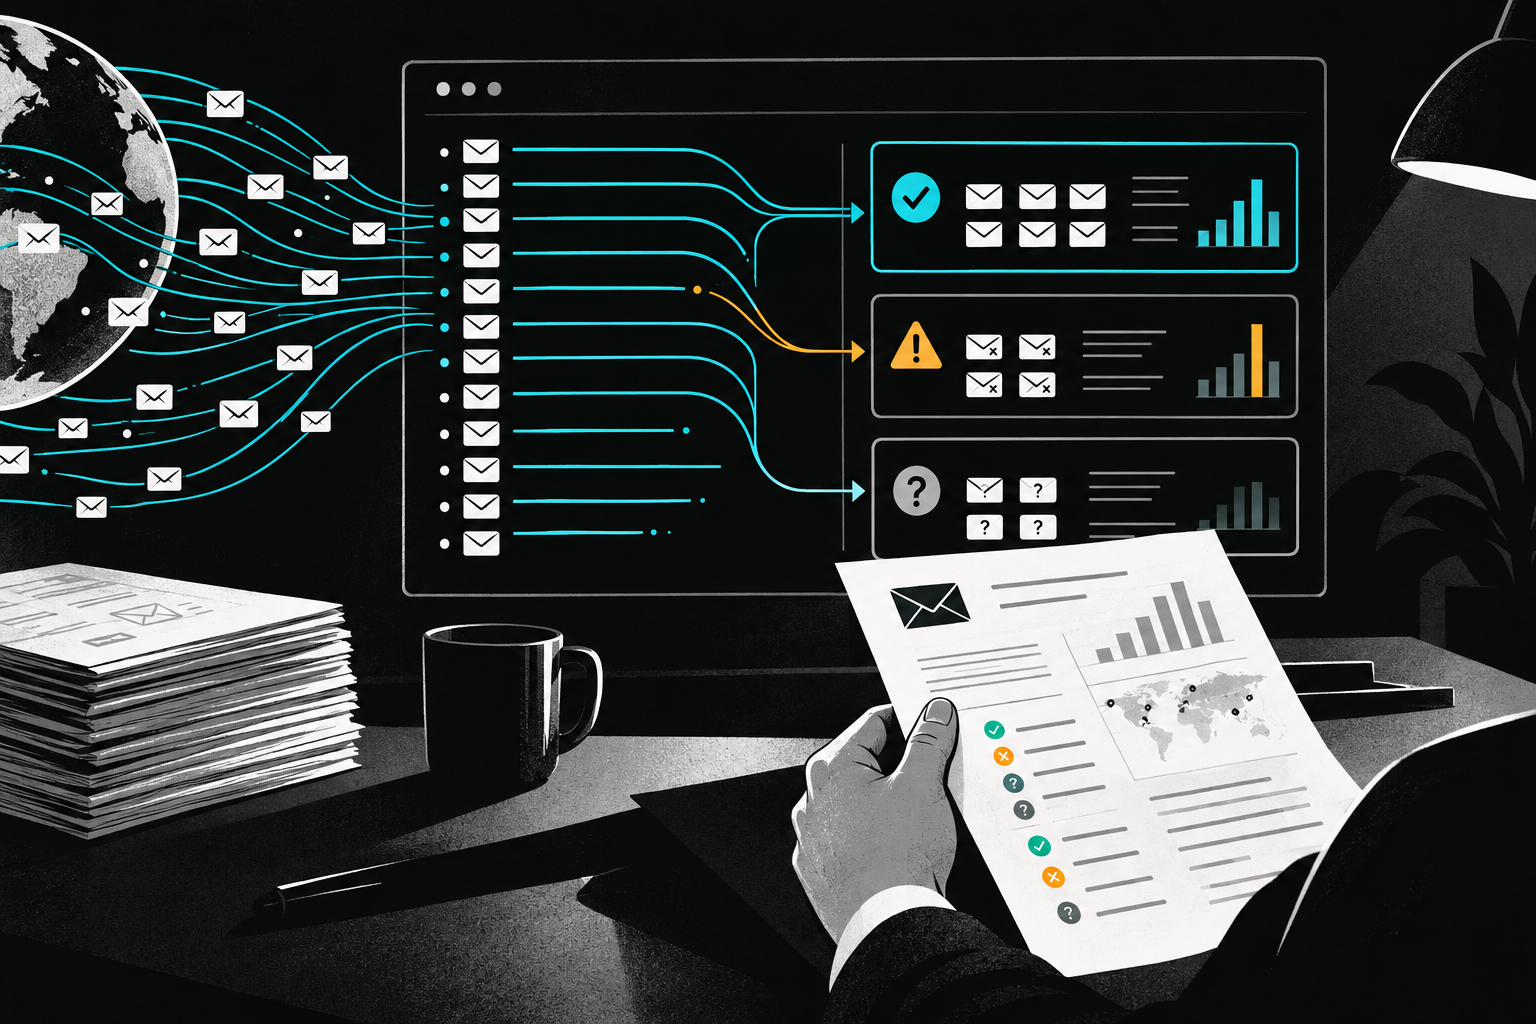
DMARC reporting turns a DNS entry into an operating practice. Reports can be dense XML, which is why many organisations use a reporting service or a dedicated mailbox. Nobody needs every employee to parse raw XML. Someone does need to review the evidence and act on anomalies.
RFC 7489 defines aggregate reporting through rua. Aggregate reports can show source IP addresses, authentication outcomes, policy evaluation, and message counts. They let the owner see mail claiming the domain, whether SPF and DKIM passed, whether alignment succeeded, and which sources were involved.
Classify entries before editing DNS:
- Known and passing. A recognised provider sends expected traffic with aligned SPF or DKIM.
- Known but failing. A recognised provider sends legitimate mail but does not satisfy DMARC.
- Unknown but plausibly legitimate. Investigate: it may be a forgotten service, agency, application, or infrastructure change.
- Unknown and unauthorised. The business has no reason to permit that use of its domain.
Known but failing traffic is the immediate rollout priority. Under p=none, customers may still receive some of that mail, but the sender has not established an aligned identity. Repair it before tightening policy.
Unknown traffic is why review continues after enforcement. A report is evidence that a source sent mail claiming the domain and how a receiver evaluated it. It does not prove malicious intent. Shared infrastructure, forwarding, and third parties can complicate attribution. Investigate before assigning a cause.
After initial stabilisation, a monthly review is often enough for a small business. Review more often after DNS changes, a new sending platform, a campaign launch, or a material provider change.
Use a short review checklist:
- Do expected senders appear in reports, provider records, and headers? Investigate missing or unrecognised sources.
- Do expected messages pass DMARC? Correct the return path, signing domain, or From configuration if they do not.
- Does policy match the rollout stage? Make a deliberate update with tests and a rollback plan.
- Does someone own report review? Assign an operational owner if not.
- Have retired services been removed from vendor lists, SPF, DKIM, and reports? Remove authorisations and document the change.
Read reports alongside real-message tests. Send mail from each approved service to test mailboxes at major providers and inspect received headers. Confirm visible From, SPF, DKIM, and DMARC outcomes. A report identifies patterns; headers show a concrete recipient evaluation.
Reports are not a universal deliverability dashboard. They do not measure usefulness, customer consent, or every local filtering choice. Google and Yahoo place authentication alongside complaint rates and responsible sending. But reports answer a narrow question extremely well: who is using the domain as an email identity, and do they pass aligned authentication? That answer should precede p=quarantine or p=reject.
🖼️ The image of a trusted sender
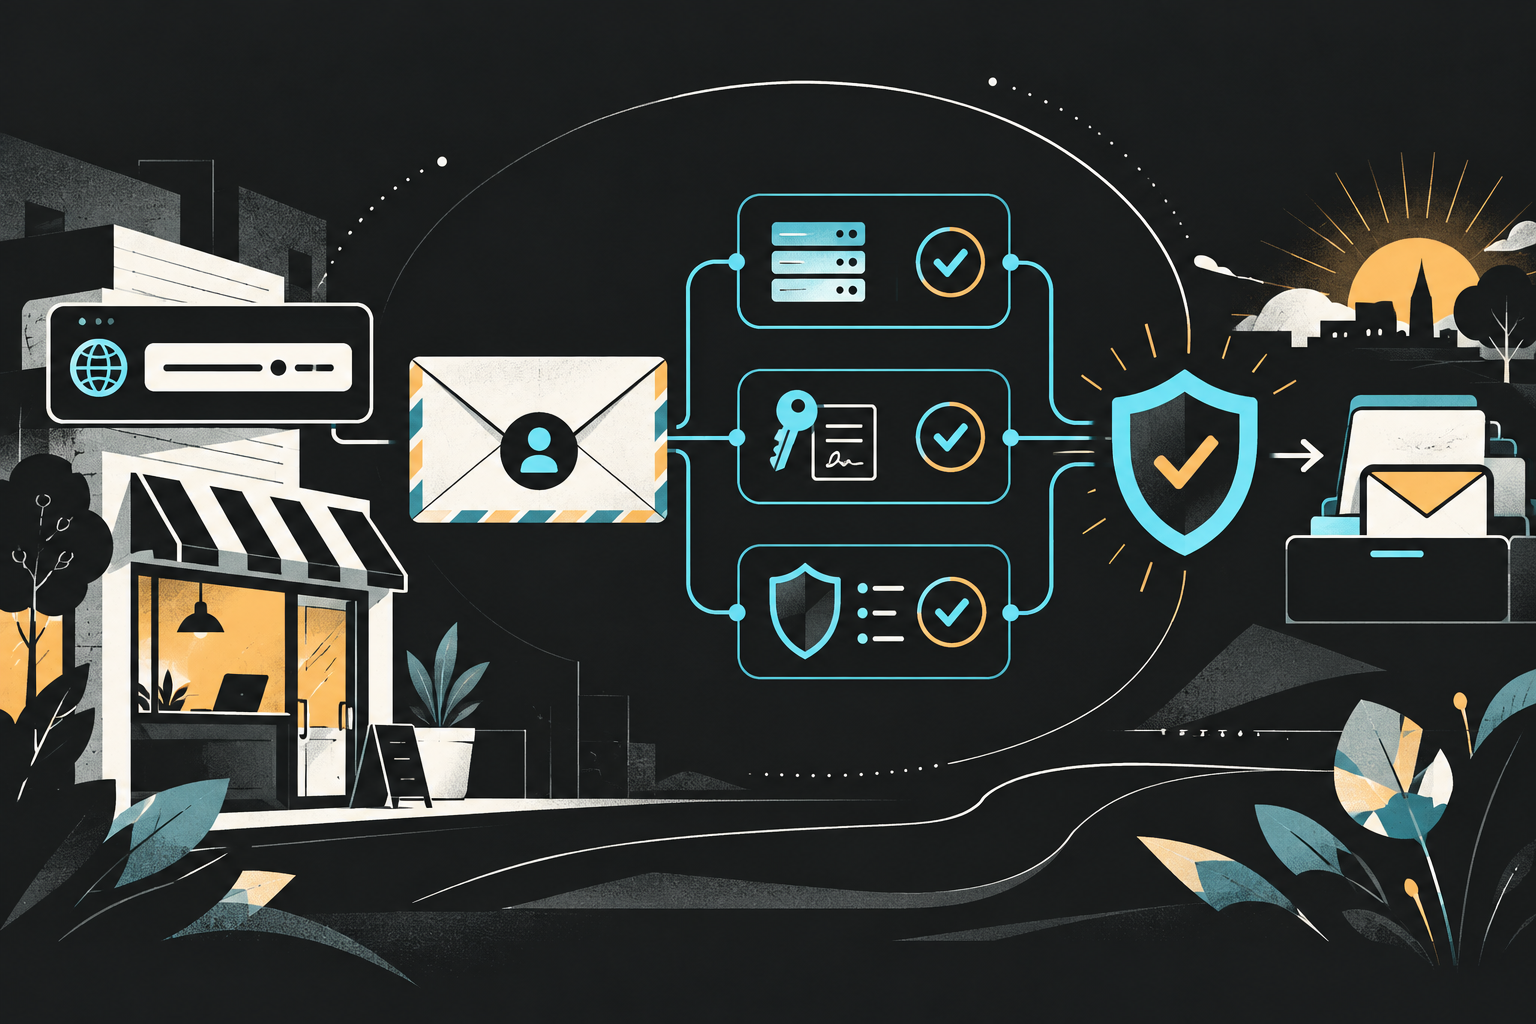
Customers do not read DMARC records. They notice whether receipts arrive, support replies consistently use the business domain, and messages carrying the company name can be distinguished from imitations.
A trusted sender image begins with consistency. Choose the visible From domain deliberately. Configure the platform so aligned SPF or DKIM authenticates it. Know why the service sends, who operates it, and how it will be retired when the relationship ends.
This matters when a business has several brands or mail functions. A marketing subdomain can give newsletter traffic a distinct identity. A transactional subdomain can separate payment or account messages. A separate domain can suit a separate brand. These are design choices, not DMARC requirements. Their value is internal accountability.
Avoid shortcuts. A display-name change does not authenticate mail. A provider claim about deliverability does not establish alignment. An SPF record copied from a help page does not prove that the visible From identity is covered. Trust comes from the combined configuration and evidence that it works.
Why it matters: DMARC connects the domain customers see in From with authenticated mail systems the owner has approved. The connection stays useful only with a sender inventory, report review, and a policy that matches the business’s actual control.
Use careful language around trust. DMARC can help receivers identify mail that fails aligned authentication and can request quarantine or rejection. It cannot certify every message as safe, prevent lookalike domains, or stop a compromised legitimate mailbox from sending harmful authenticated mail. It reduces one specific ambiguity: unauthenticated or misaligned use of the business’s own domain.
That is a concrete brand-protection gain. The business decides which services may speak for its domain and can publish a stronger preference for everyone else.
⚠️ Limits and trade-offs
DMARC is precise, and email delivery is complicated.
First, DMARC does not replace SPF or DKIM. It depends on them. A broken SPF record, unsigned message, or DKIM signature invalidated by message changes can cause DMARC failure if no other aligned mechanism passes. Find the mail flow and configure an aligned path rather than weakening policy by default.
Second, forwarding can complicate SPF. RFC 7489 discusses indirect mail flows: forwarding can change the path from which a receiver evaluates SPF. DKIM may provide an aligned pass if the signature stays valid, but modified signed content can invalidate it. Do not depend on one test or one mechanism.
Third, DMARC does not command every receiver. RFC 7489 calls policy a request and allows local receiver decisions. Google and Yahoo publish their own requirements; other recipients can decide differently. Describe DMARC as a widely used domain-authentication policy mechanism, not universal inbox control.
Fourth, report data needs handling rules. RFC 7489 discusses privacy and reporting considerations, especially for failure reporting. Aggregate reports are the normal starting point. Decide who receives them, how long they are retained, and whether an external service meets the business’s security and privacy needs.
Fifth, p=reject can expose neglected systems. That is useful only after discovery. If an old application sends password resets using an unauthenticated From address, receivers applying rejection may refuse it. Fix or replace the sender, or give the flow an appropriately authenticated identity. Do not leave the domain permanently unprotected because an unknown system might exist.
Manage the trade-off through scope and timing: use reports, verify providers, separate streams where helpful, use pct where staged application is appropriate, keep a change log, and test providers before launch. Those are operating disciplines, not one-time DNS tasks.
Do not tell customers or staff that “DMARC guarantees delivery” or “DMARC stops phishing.” The cited material supports neither claim. A fair statement is narrower: DMARC lets a domain owner publish a requested policy for mail that fails aligned SPF and DKIM checks; stronger policies can help protect the domain from unauthenticated use where receivers apply them.
✅ The decision to make this week
The decision is not whether the business will become an email-security specialist. It is whether it will own the identity attached to outbound mail.
Start with the domain customers see. List every system that sends with it: mail host, web forms, accounting platform, support tool, calendar system, ecommerce notices, recruitment software, and agency-managed service. For each, identify the visible From domain, SPF identity, DKIM signing domain, technical owner, business purpose, and review date.
Then publish or review the DMARC record at _dmarc. If senders are not mapped, begin with p=none and an aggregate-report destination somebody reads. Google accepts p=none as the minimum bulk-sender policy; CISA’s BOD 18-01 shows the value of a monitored route toward enforcement. Use the observation period to correct alignment, not to announce completion.
Set a review date before publishing. The resulting decision should be evidence-based: remain in observation because a named legitimate problem is being fixed; move to p=quarantine because known traffic aligns; or advance to p=reject because authorised use is understood and the business is ready to request rejection of failures. Record why.
A compact starting list:
- Assign one owner for DNS policy and one for report review. They can be the same person.
- Inventory every approved sender using the domain in From.
- Verify SPF and DKIM in real received messages.
- Confirm an aligned passing result for each approved sender.
- Publish
p=nonewith a monitored aggregate-report address if no DMARC record exists. - Review reports and fix known failures.
- Set a dated route to
p=quarantineand thenp=rejectwhen evidence supports it. - Add authentication review to email-vendor onboarding and offboarding.
Do not wait for a delivery failure or spoofed message to learn which systems speak for the domain. Establish the list, read the evidence, and move from visibility to a policy that reflects real control.
*Sources: Google Email sender guidelines; Yahoo sender best practices; DMARC overview; CISA Binding Operational Directive 18-01; RFC 7489: Domain-based Message Authentication, Reporting, and Conformance.*


